/capture-screenshots
Authoring class
Writes exactly one artifact into the repo, then proposes the commit — never runs git itself. Shared rules: CONVENTIONS-authoring.md.
Captures from a running web app, terminal/CLI output, a static HTML/component, or existing images, then runs a redaction pipeline (detect PII/secrets → blur/mask → verify) so nothing sensitive ships. Writes redacted images into docs and PROPOSES the commit; the un-redacted original never gets committed.
At a glance
| Run it | /capture-screenshots |
| Class | authoring |
| Version | 0.1.0 |
| Author | navjyotnishant |
| Cost | a 3-agent pipeline (capturer → sensitive-data-reviewer → redactor) per image |
| Needs | Playwright (via npx) · sharp or jimp (via npx) |
| Source | skills/capture-screenshots/SKILL.md |
What it needs, and what happens without it
Every tool is detected at runtime — none is installed for you.
| Tool | Without it |
|---|---|
Playwright (via npx) |
ask for an existing image, or capture terminal/component output instead |
sharp or jimp (via npx) |
BLOCK — an unredacted image must never be written |
The pipeline
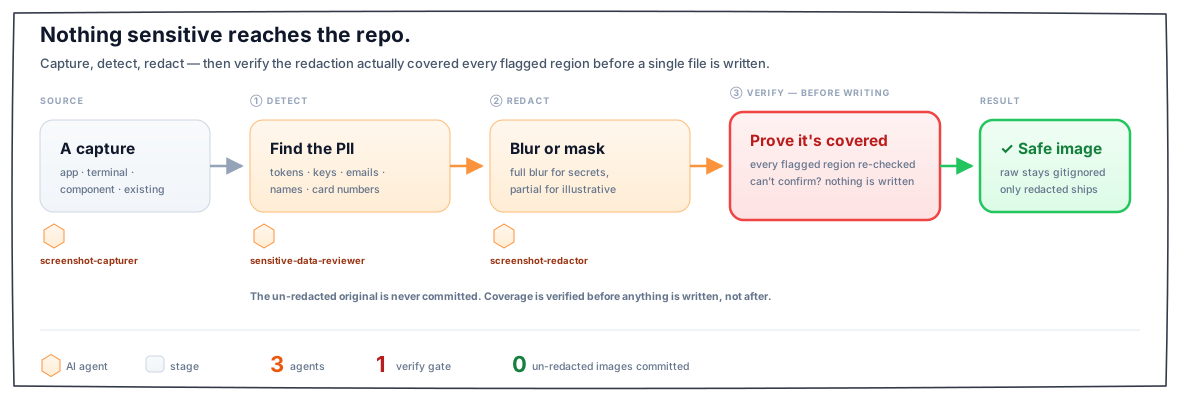
Agents it spawns
screenshot-capturer— Capture a screenshot from one of four sources — a running web app (Playwright), terminal/CLI output rendered…screenshot-redactor— Redact sensitive regions in a screenshot — full blur / solid box for high-risk (tokens, keys, cards, SSNs)…sensitive-data-reviewer— Inspect a screenshot for sensitive data — emails, API keys/tokens, passwords, phone numbers, credit-card/SSN…
The procedure
The executable steps live in the skill file itself and are deliberately not reproduced here: they are instructions to the model at runtime, not documentation.