/security-deep-review
Review class · gate
Advise only. Reads changes, reports findings, and never writes a file or commits. Shared rules: CONVENTIONS.md.
Runs the same mandatory secret-scanner gate first, then a Workflow-tool pipeline — parallel specialist finders sweep independent lenses (injection/authz, SSRF/deserialization/path-traversal, supply-chain, crypto/authn, cloud/infra), each finding is adversarially re-checked by independent verifiers (majority-refute kills it), then one synthesis pass produces a severity-ranked BLOCK/WARN/PASS report. Diff-scoped by default; --full sweeps the whole repo. Deliberately invoked, not part of the default pre-push fleet.
At a glance
| Run it | /security-deep-review |
| Class | review · gate |
| Version | 0.1.0 |
| Author | navjyotnishant |
| Cost | typically 5 finder calls + up to 15 verifier calls (commonly 15–30 total agent calls for a mid-size diff) |
| Needs | gitleaks or trufflehog or detect-secrets |
| Source | skills/security-deep-review/SKILL.md |
What it needs, and what happens without it
Every tool is detected at runtime — none is installed for you.
| Tool | Without it |
|---|---|
gitleaks or trufflehog or detect-secrets |
BLOCK with install instructions — the gate cannot be skipped |
The pipeline
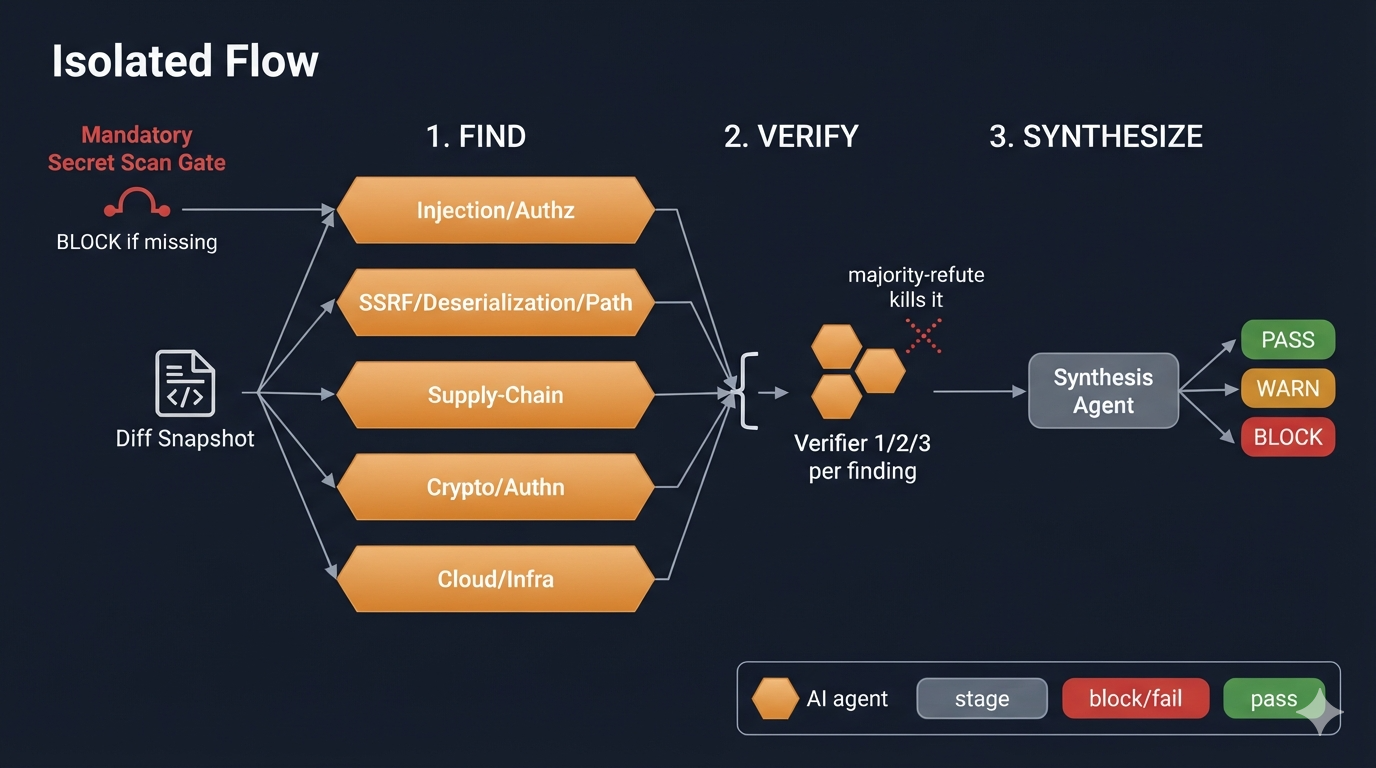
Agents it spawns
security-finder— Use this agent as one of several parallel lens-scoped finders in the security-deep-review Workflow pipeline —…security-verifier— Use this agent as an independent adversarial verifier in the security-deep-review Workflow pipeline — given…
The procedure
The executable steps live in the skill file itself and are deliberately not reproduced here: they are instructions to the model at runtime, not documentation.