/deps-upgrade
Review class · scan
Advise only. Reads changes, reports findings, and never writes a file or commits. Shared rules: CONVENTIONS.md.
Surveys the WHOLE current dependency manifest for available upgrades, flags each with a semver risk class and breaking-change signals, and proposes a prioritized upgrade plan — it never runs the upgrade or edits the manifest. Detects the repo's package manager at runtime; zero-network by default.
At a glance
| Run it | /deps-upgrade |
| Class | review · scan |
| Version | 0.1.0 |
| Author | navjyotnishant |
| Cost | 1–2 agent calls |
| Needs | the repo's package manager (npm, pip, cargo, go) |
| Source | skills/deps-upgrade/SKILL.md |
What it needs, and what happens without it
Every tool is detected at runtime — none is installed for you.
| Tool | Without it |
|---|---|
the repo's package manager (npm, pip, cargo, go) |
manifest-only survey; say the data is from the manifest, not the registry |
The pipeline
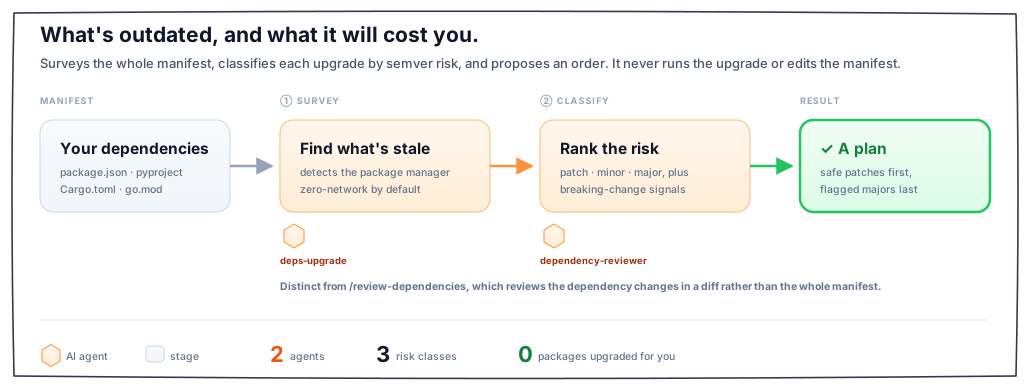
Agents it spawns
dependency-reviewer— Review dependency-manifest and license changes in a code diff — added/removed/upgraded packages, license…deps-upgrade— Survey a project's current dependency manifest for available upgrades and propose a prioritized upgrade plan…
The procedure
The executable steps live in the skill file itself and are deliberately not reproduced here: they are instructions to the model at runtime, not documentation.